

AI in Cybersecurity: Friend or Foe? | AI-Powered Threats & Defenses
Artificial Intelligence (AI) has rapidly become a defining force in cybersecurity. It’s a double-edged sword: while defenders leverage AI to detect threats and respond faster, attackers use the same technology to scale, automate, and sophisticate their attacks.
As businesses adopt AI across industries, the question is no longer “Should we use AI in cybersecurity?” but rather, “How do we stay ahead of adversaries who already are?”
AI’s Expanding Role in Cybersecurity
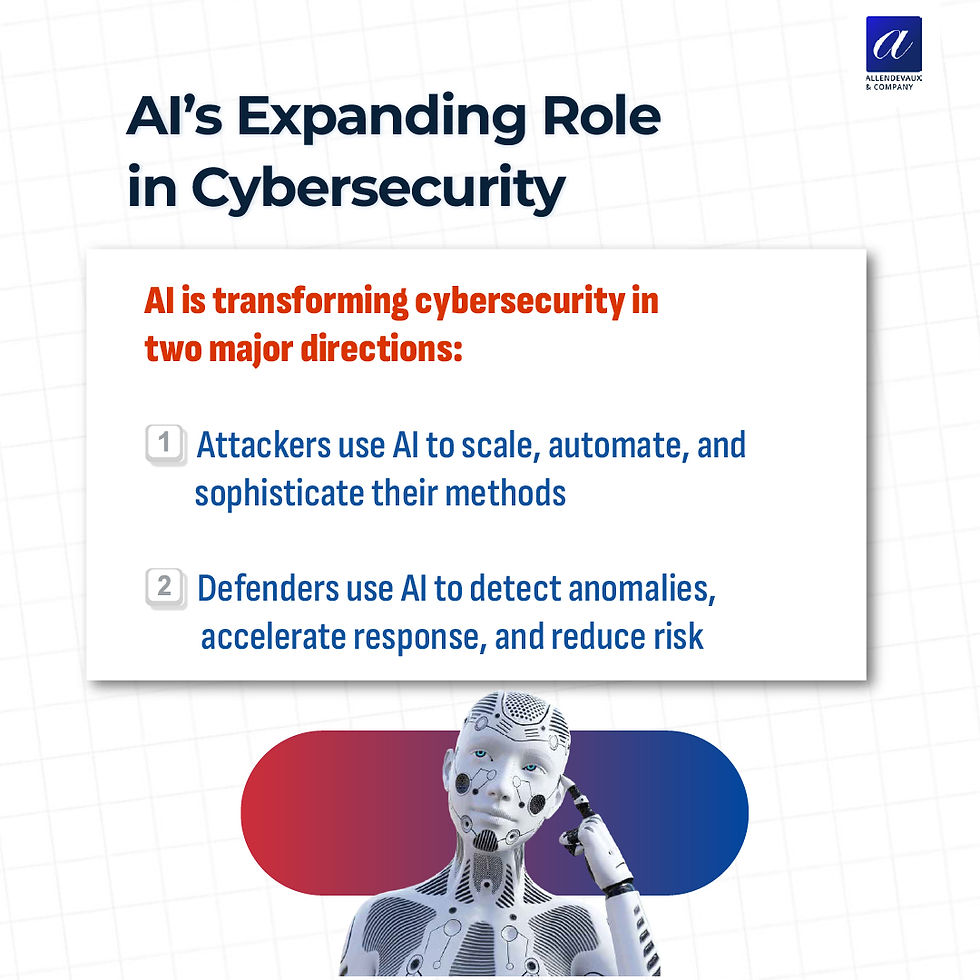
AI is transforming cybersecurity in two critical directions:
Attackers’ Advantage: Hackers exploit AI to launch large-scale phishing campaigns, generate malware scripts, and manipulate trust through deepfake voices and videos. Machine Learning (ML) even helps them discover zero-day vulnerabilities faster than humans can.
Defenders’ Shield: Security teams rely on AI to detect anomalies, reduce false positives, accelerate incident response, and automate vulnerability management.
This dual role makes AI one of the most disruptive — and essential — tools in the cybersecurity battlefield.
The AI Tech Stack You Need to Understand
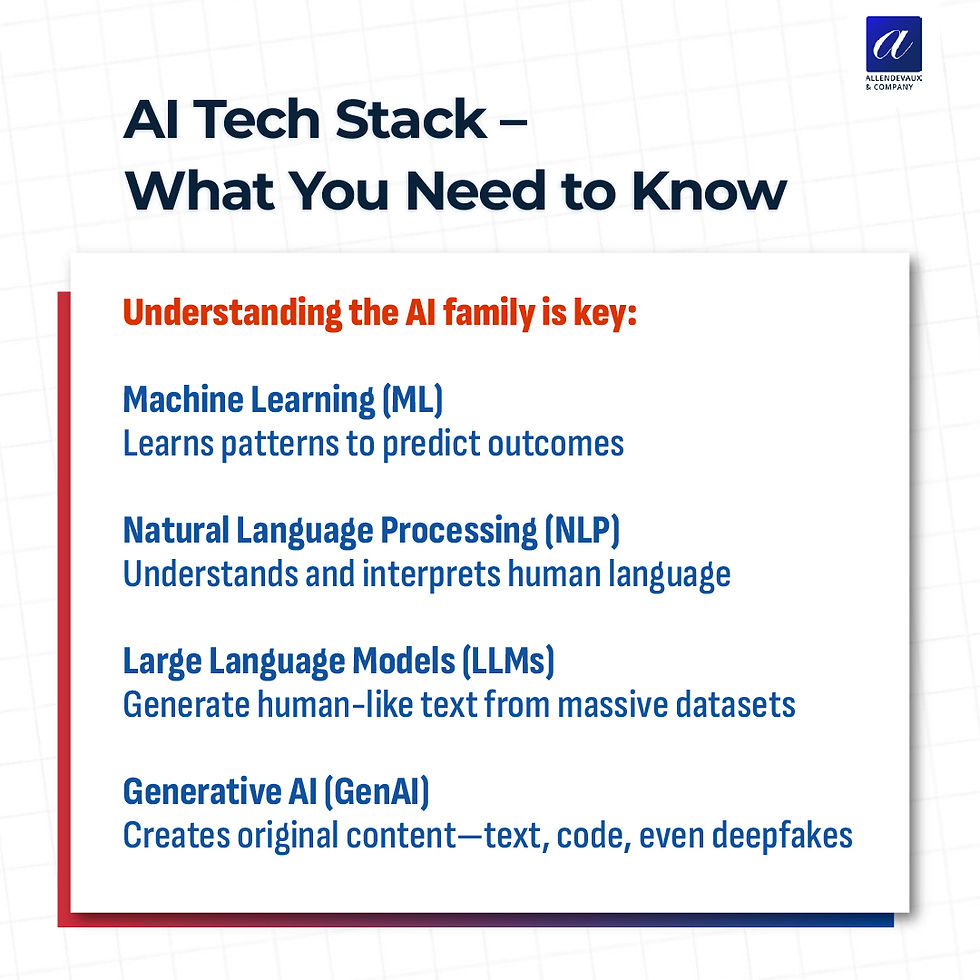
To build resilience, businesses must understand the AI technologies driving modern cybersecurity:
Machine Learning (ML): Identifies patterns and predicts malicious behavior.
Natural Language Processing (NLP): Processes and interprets human language, making alert triage and phishing detection more effective.
Large Language Models (LLMs): Generate human-like text, which attackers use for phishing but defenders use for automated reporting.
Generative AI (GenAI): Creates original text, code, or media — enabling both deepfake scams and automated security scripts.
By knowing how each layer functions, organizations can apply AI strategically while anticipating how adversaries may abuse it.
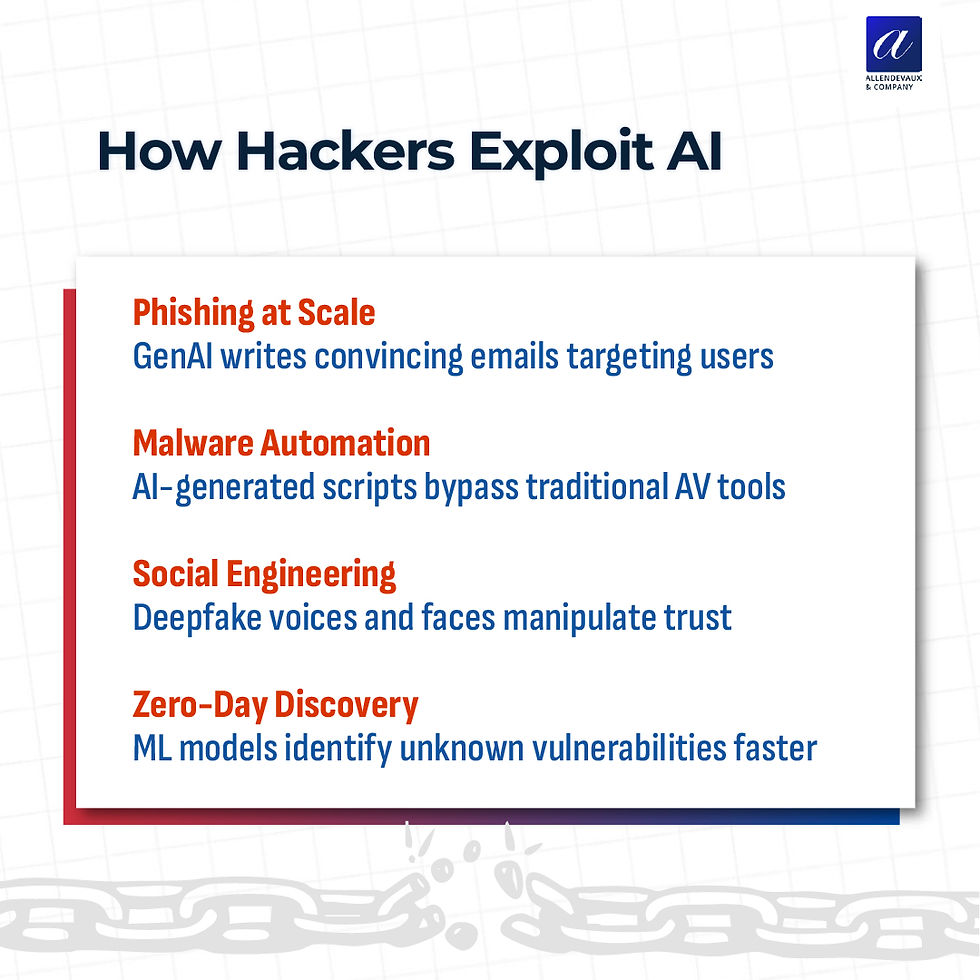
How Hackers Exploit AI
Cybercriminals waste no time adopting AI. Some of their most common tactics include:
Phishing at Scale: Generative AI produces convincing, error-free emails that bypass traditional detection.
Malware Automation: AI writes or obfuscates code that avoids signature-based antivirus tools.
Social Engineering: Deepfake technology impersonates executives or trusted contacts to manipulate victims.
Zero-Day Discovery: ML accelerates vulnerability hunting, giving attackers a head start.
These tactics highlight why AI-driven threats are faster, smarter, and more dangerous than traditional cyberattacks.
How Security Teams Use AI
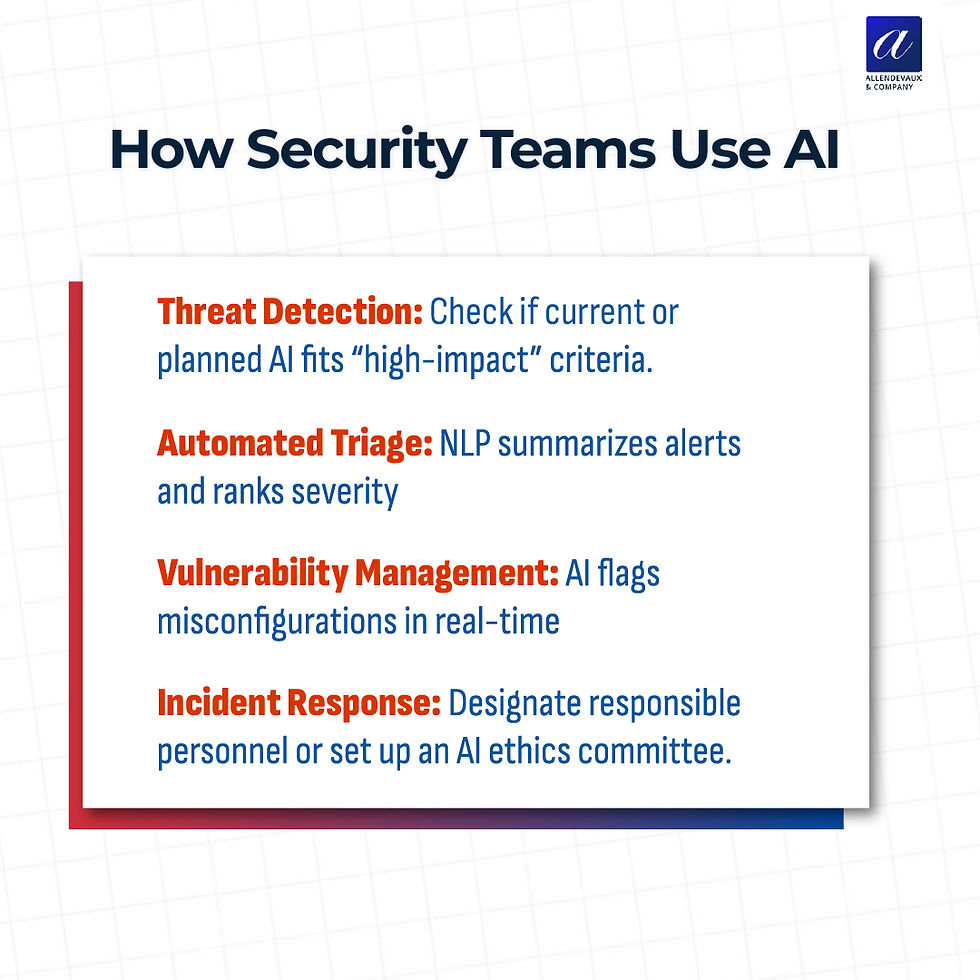
Fortunately, defenders are equally empowered by AI. Cybersecurity teams deploy AI to:
Threat Detection: Identify anomalies and high-impact risks in real-time.
Automated Triage: NLP summarizes alerts and prioritizes severity, reducing alert fatigue.
Vulnerability Management: AI continuously scans for misconfigurations and exposures.
Incident Response: GenAI generates containment scripts, assists in forensic code analysis, and even supports SOC workflows via ChatOps.
This not only reduces response times but also enables organizations to defend at scale — a crucial advantage against AI-powered adversaries.
GenAI in the Battle of Code
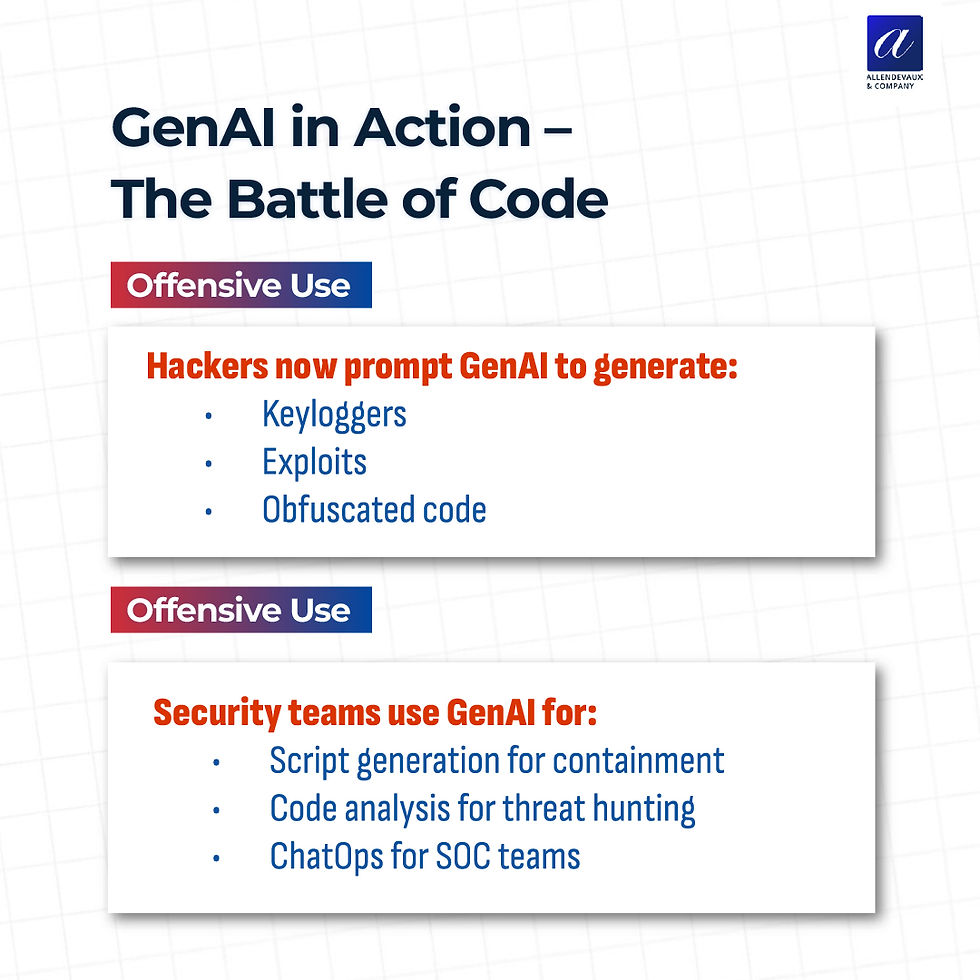
Perhaps the clearest example of AI’s dual role is in code.
Offensive Use: Hackers prompt GenAI to write keyloggers, exploits, and obfuscated scripts.
Defensive Use: Security teams harness the same tools for automated script generation, reverse engineering malware, and building smarter detection logic.
The reality is that Generative AI accelerates both attack frequency and defense capability. The difference lies in how prepared your security teams are to deploy it effectively.
Why AI-Driven Cybersecurity is Mission-Critical
The stakes are rising. With increasing attack sophistication and widespread SOC challenges such as alert fatigue, talent shortages, and resource constraints, integrating AI into your security stack is no longer optional — it’s mission-critical.
Organizations that fail to adopt AI-driven cybersecurity risk falling behind attackers who are already exploiting these tools. Conversely, those that embrace AI strategically can gain visibility, speed, and resilience.
Final Thoughts: Friend or Foe?
AI in cybersecurity is both — it’s a friend to defenders and a powerful weapon for attackers. The difference lies in who wields it more effectively.
At Allendevaux and Company, we help organizations harness AI as a force for good. From AI-powered threat detection to automated incident response, we ensure your business stays one step ahead of adversaries.
👉 Ready to strengthen your defenses with AI? Contact us today and future-proof your cybersecurity strategy.


Chủ đề này có vẻ khó vì cùng một hệ thống AI có thể tạo ra rủi ro lẫn hỗ trợ bảo vệ. Tựa đề đặt đúng câu hỏi khiến người đọc không thể nhìn công nghệ theo một hướng duy nhất. Tôi chú ý nhất đến sự cân bằng giữa năng lực của công cụ và cách tk88 con người quyết định sử dụng chúng. Càng nhiều hoạt động dựa vào hệ thống số, chuyện an toàn mạng càng gần với đời thường, chứ không chỉ là đề tài dành riêng cho chuyên gia.
Bài về AI trong an ninh mạng làm tôi nghĩ đến tin nhắn của bạn thân về các mối đe dọa mới. Người đó từng nhắc Game bài đổi thưởng và có nói tai xiu như ví dụ về tên gọi lạ, còn tôi thì thấy vấn đề nằm ở cách người dùng phản ứng. AI vừa hỗ trợ vừa gây rủi ro, bài đặt câu hỏi đúng. Tôi chưa rõ doanh nghiệp nhỏ nên bắt đầu từ đâu, chỉ biết cần cập nhật kiến thức thường xuyên. Không nên tin tuyệt đối vào công cụ tự động.
Điểm tôi thấy đáng chú ý là trí tuệ nhân tạo trong an ninh mạng không hẳn đứng về một phía. Cùng một công cụ có thể hỗ trợ phát hiện bất thường nhưng cũng khiến thủ đoạn giả mạo khó nhận ra hơn. Đọc đoạn nói về dữ liệu và tài khoản, tôi nhớ lần bạn bè bàn về game bài đổi thưởng, trong đó cái tên sunwin được nhắc khi câu chuyện chuyển sang rủi ro lộ thông tin trên môi trường mạng. Tôi chỉ nghe vậy chứ chưa rõ nền tảng này hoạt động ra sao. Bài viết làm tôi nghĩ nhiều hơn về thói quen cảnh giác, thay vì nhìn trí tuệ nhân tạo như một giải…
Bài viết đặt câu hỏi về việc AI trong an ninh mạng là bạn hay kẻ thù, rồi mở ra cả hai mặt của công nghệ: hỗ trợ phát hiện nguy cơ nhưng cũng có thể bị lạm dụng. Tôi thấy phần này gần với đời sống hơn tưởng tượng, vì ngay cả các trò chơi trực tuyến cũng khiến người ta quan tâm đến tài khoản và dữ liệu cá nhân. Một lần nghe bạn bè bàn về game bài đổi thưởng, tôi có nghe tên TN88, nhưng không biết đủ để đánh giá nền tảng nào. Vì vậy, điều tôi giữ lại sau bài là sự thận trọng trước công nghệ, không phải một kết luận đơn giản…
Đọc bài về AI trong an ninh mạng, tôi bị cuốn vào câu hỏi AI là bạn hay thù, nhất là khi các mối đe dọa cũng dùng công cụ tương tự. Tối hôm qua, trong lúc chờ tải bản vá, một đồng nghiệp có kể rằng anh từng nghe nhắc Game bài đổi thưởng và JW88.com trong một cuộc trò chuyện về lừa đảo trực tuyến, nhưng cả hai chúng tôi đều chưa rõ thực hư. Tôi không kết luận gì thêm, chỉ thấy bài viết nhắc đúng cảm giác vừa muốn tự động hóa vừa phải giữ cảnh giác; công nghệ càng tiện thì càng cần kiểm tra lại những thứ tưởng như quen thuộc.